Chasing a network error
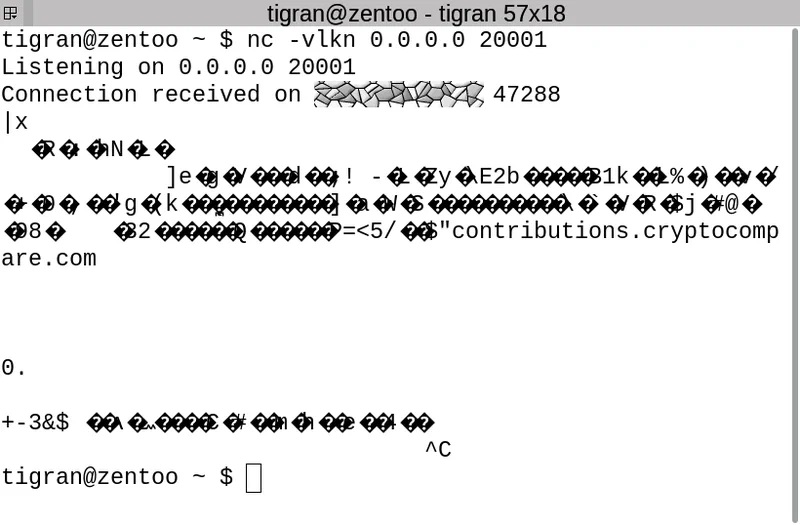
TLS Handshake dumped to terminal. SNI shows in plain text the intended destination FQDN.
These things happen sometimes in production.
The log shows an error connecting to a certain IP address, which is not found in the source tree.
It is a typical node.js project that has too many dependencies to make sense of.
So, how to find the piece referring to the error?
The difficulty is caused by the code using an unknown FQDN. I needed more information, more context to figure out whether this is malicious activity, or maybe an outdated feature that should have been removed already.
The actual error looks like the following.
1Error: connect ECONNREFUSED 217.182.242.104:443
2    at TCPConnectWrap.afterConnect [as oncomplete] (net.js:1054:14) {
3  errno: 'ECONNREFUSED',
4  code: 'ECONNREFUSED',
5  syscall: 'connect',
6  address: '217.182.242.104',
7  port: 443
8}
After trying and failing to find useful information by reverse DNS lookup, I went straight ahead and redirected that connection to an IP address controlled by me, using iptables.
1iptables -t nat -A OUTPUT -p tcp --dport 443 --dst 217.182.242.104 -j DNAT --to-destination 3.3.3.3:20001
The 3.3.3.3 here is a placeholder for my own IP.
The rest is shown in the main image - a simple netcat will listen for and accept that connection, and will display the missing detail - the domain name, which leads to the exact portion of the code.
P.S.
To undo the iptables rule, replace the -A with -D.
1iptables -t nat -D OUTPUT -p tcp --dport 443 --dst 217.182.242.104 -j DNAT --to-destination 3.3.3.3:20001
And, if it were not the same machine but the corresponding router, it should have been the FORWARD chain, instead of OUTPUT.